Security by Design, Proven in Production
We build mission-critical technology with layered security controls, customer data isolation, and continuous vulnerability assessment.
How we protect the systems we build
Explore the identity, delivery, and data protection practices that shape our engineering work.
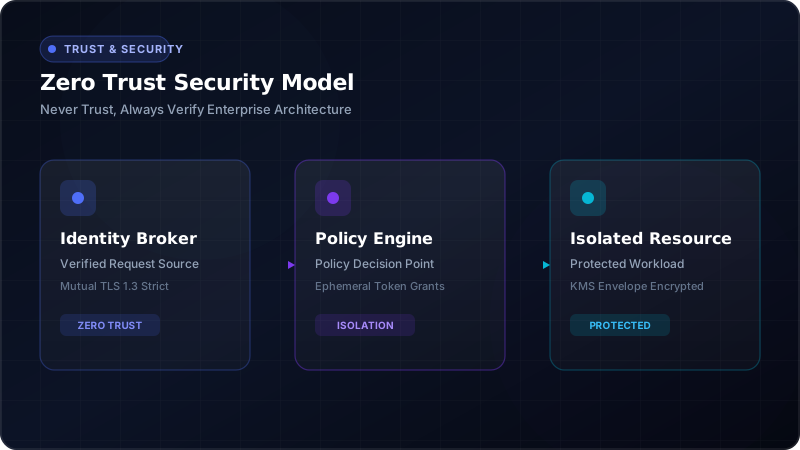
Zero Trust Architecture
We assume breach across all network boundaries. No request is implicitly trusted based on its origin or location. Every interaction requires verified cryptographic identity, mutual TLS 1.3 encryption, and ephemeral token-scoped authorization.
- Strict Mutual TLS (mTLS 1.3) service-to-service communication.
- Short-lived JWT & OIDC token rotation with zero long-lived static secrets.
- Micro-segmented virtual private clouds (VPCs) with zero direct database exposure.
Automated Secure SDLC
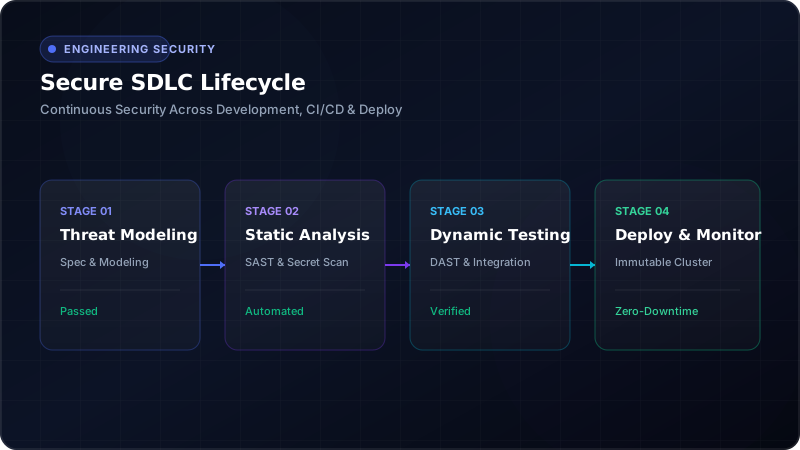
Security is not a final audit step; it is embedded into every commit and pull request. Automated static analysis (SAST), software composition analysis (SCA), and container vulnerability scans block builds before merge.
- Automated secret scanning preventing accidental token leaks in Git.
- Hermetic container builds with signed Software Bill of Materials (SBOM).
- Mandatory peer code review by senior engineers for all production paths.
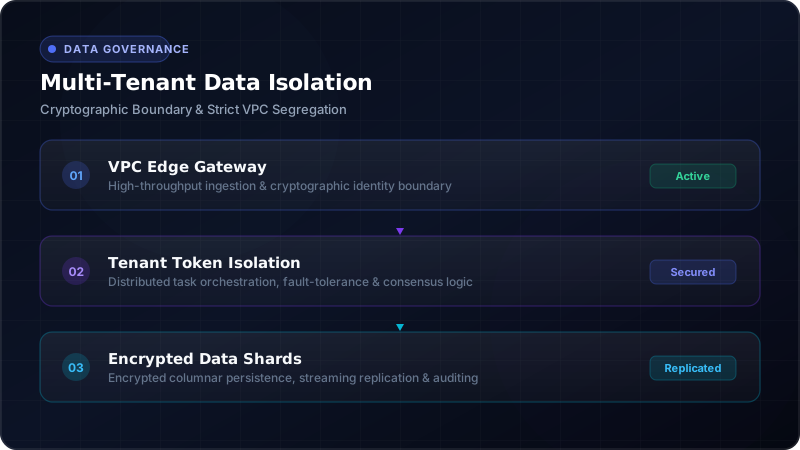
Cryptographic Data Isolation
Customer data is protected using AES-256 envelope encryption at rest and TLS 1.3 in transit. Multi-tenant architectures employ strict row-level security (RLS) policies and dedicated tenant KMS keys.
- Dedicated customer encryption keys managed via AWS KMS or Azure Key Vault.
- Granular role-based access control (RBAC) with principle of least privilege.
- Comprehensive audit logging streamed to immutable WORM storage.
Enterprise Governance & Controls
Our operational standards protect your business, customer privacy, and intellectual property.
100% IP Ownership
You own all custom code, architectures, trained adapters, and design systems from inception. No proprietary vendor lock-in.
Vulnerability Disclosure
We welcome responsible security research. Identified vulnerabilities are triaged by our core security team within 24 hours.
Cloud Agnostic
Deploy securely across AWS, Microsoft Azure, Google Cloud Platform, or private air-gapped on-premise Kubernetes clusters.
24/7 Security Operations
Real-time automated alert telemetry, uptime monitoring, and SLA-backed incident response protocols for enterprise retainers.
Trust & security questions
-
No. SOC 2 Type II and ISO 27001 are in progress. We do not claim current certification. The controls on this page describe our present engineering practices.
-
We use encryption in transit and at rest, tenant-level access controls, and customer-specific encryption keys where the project architecture requires them. The exact controls are reviewed against each project's data and hosting needs.
-
Access is designed around verified identity and least privilege. We use scoped authorization and role-based permissions so people and services receive only the access their work requires.
-
You own the custom code, architecture, trained adapters, and design systems created for your project, as described in your agreement. We design for handover without proprietary vendor lock-in.
-
Send the details to info@bitneka.com. Our security team triages reported vulnerabilities within 24 hours.
-
Yes. Share your security questionnaire, data handling requirements, deployment environment, and any NDA needs through our contact page so the team can review the relevant controls with you.
Discuss your security requirements
Have specific compliance questions, a vendor security questionnaire, or NDA requirements? Bring those details to the conversation so our engineering team can address the controls relevant to your project.