Security by Design, Proven in Production
Bitneka builds mission-critical technology with defense-in-depth principles. Our engineering culture combines automated cryptographic controls, strict multi-tenant isolation, and continuous vulnerability assessment.
Zero Trust Architecture
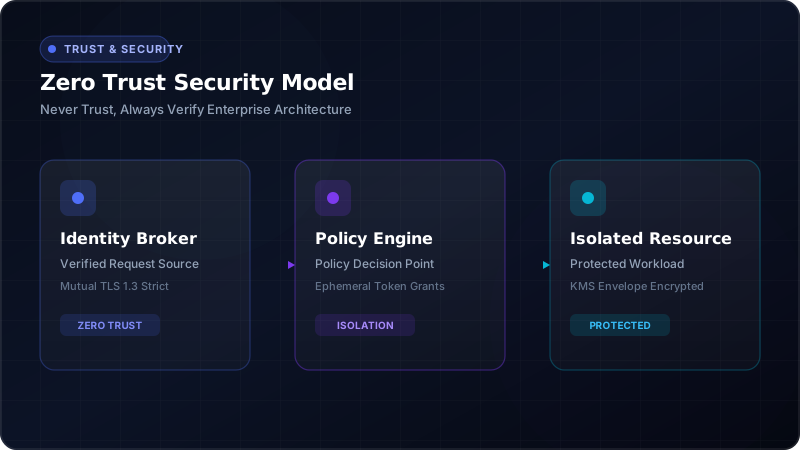
We assume breach across all network boundaries. No request is implicitly trusted based on its origin or location. Every interaction requires verified cryptographic identity, mutual TLS 1.3 encryption, and ephemeral token-scoped authorization.
- Strict Mutual TLS (mTLS 1.3) service-to-service communication.
- Short-lived JWT & OIDC token rotation with zero long-lived static secrets.
- Micro-segmented virtual private clouds (VPCs) with zero direct database exposure.
Automated Secure SDLC
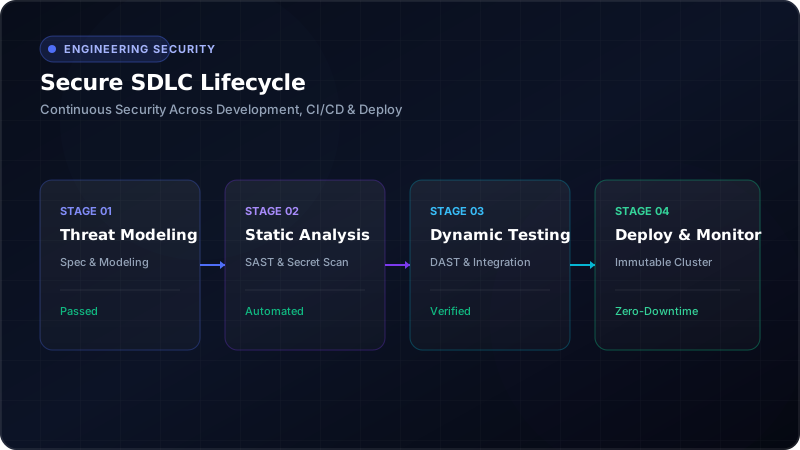
Security is not a final audit step; it is embedded into every commit and pull request. Automated static analysis (SAST), software composition analysis (SCA), and container vulnerability scans block builds before merge.
- Automated secret scanning preventing accidental token leaks in Git.
- Hermetic container builds with signed Software Bill of Materials (SBOM).
- Mandatory peer code review by senior engineers for all production paths.
Cryptographic Data Isolation
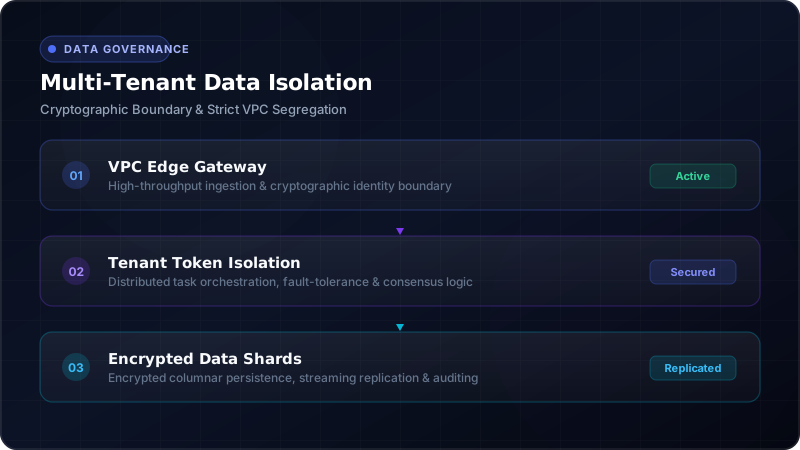
Customer data is protected using AES-256 envelope encryption at rest and TLS 1.3 in transit. Multi-tenant architectures employ strict row-level security (RLS) policies and dedicated tenant KMS keys.
- Dedicated customer encryption keys managed via AWS KMS or Azure Key Vault.
- Granular role-based access control (RBAC) with principle of least privilege.
- Comprehensive audit logging streamed to immutable WORM storage.
Enterprise Governance & Controls
Our operational standards protect your business, customer privacy, and intellectual property.
100% IP Ownership
You own all custom code, architectures, trained adapters, and design systems from inception. No proprietary vendor lock-in.
Vulnerability Disclosure
We welcome responsible security research. Identified vulnerabilities are triaged by our core security team within 24 hours.
Cloud Agnostic
Deploy securely across AWS, Microsoft Azure, Google Cloud Platform, or private air-gapped on-premise Kubernetes clusters.
24/7 Security Operations
Real-time automated alert telemetry, uptime monitoring, and SLA-backed incident response protocols for enterprise retainers.
Request a Technical Security Audit
Have specific compliance questions, vendor security questionnaires, or custom NDA requirements? Contact our engineering leadership directly.